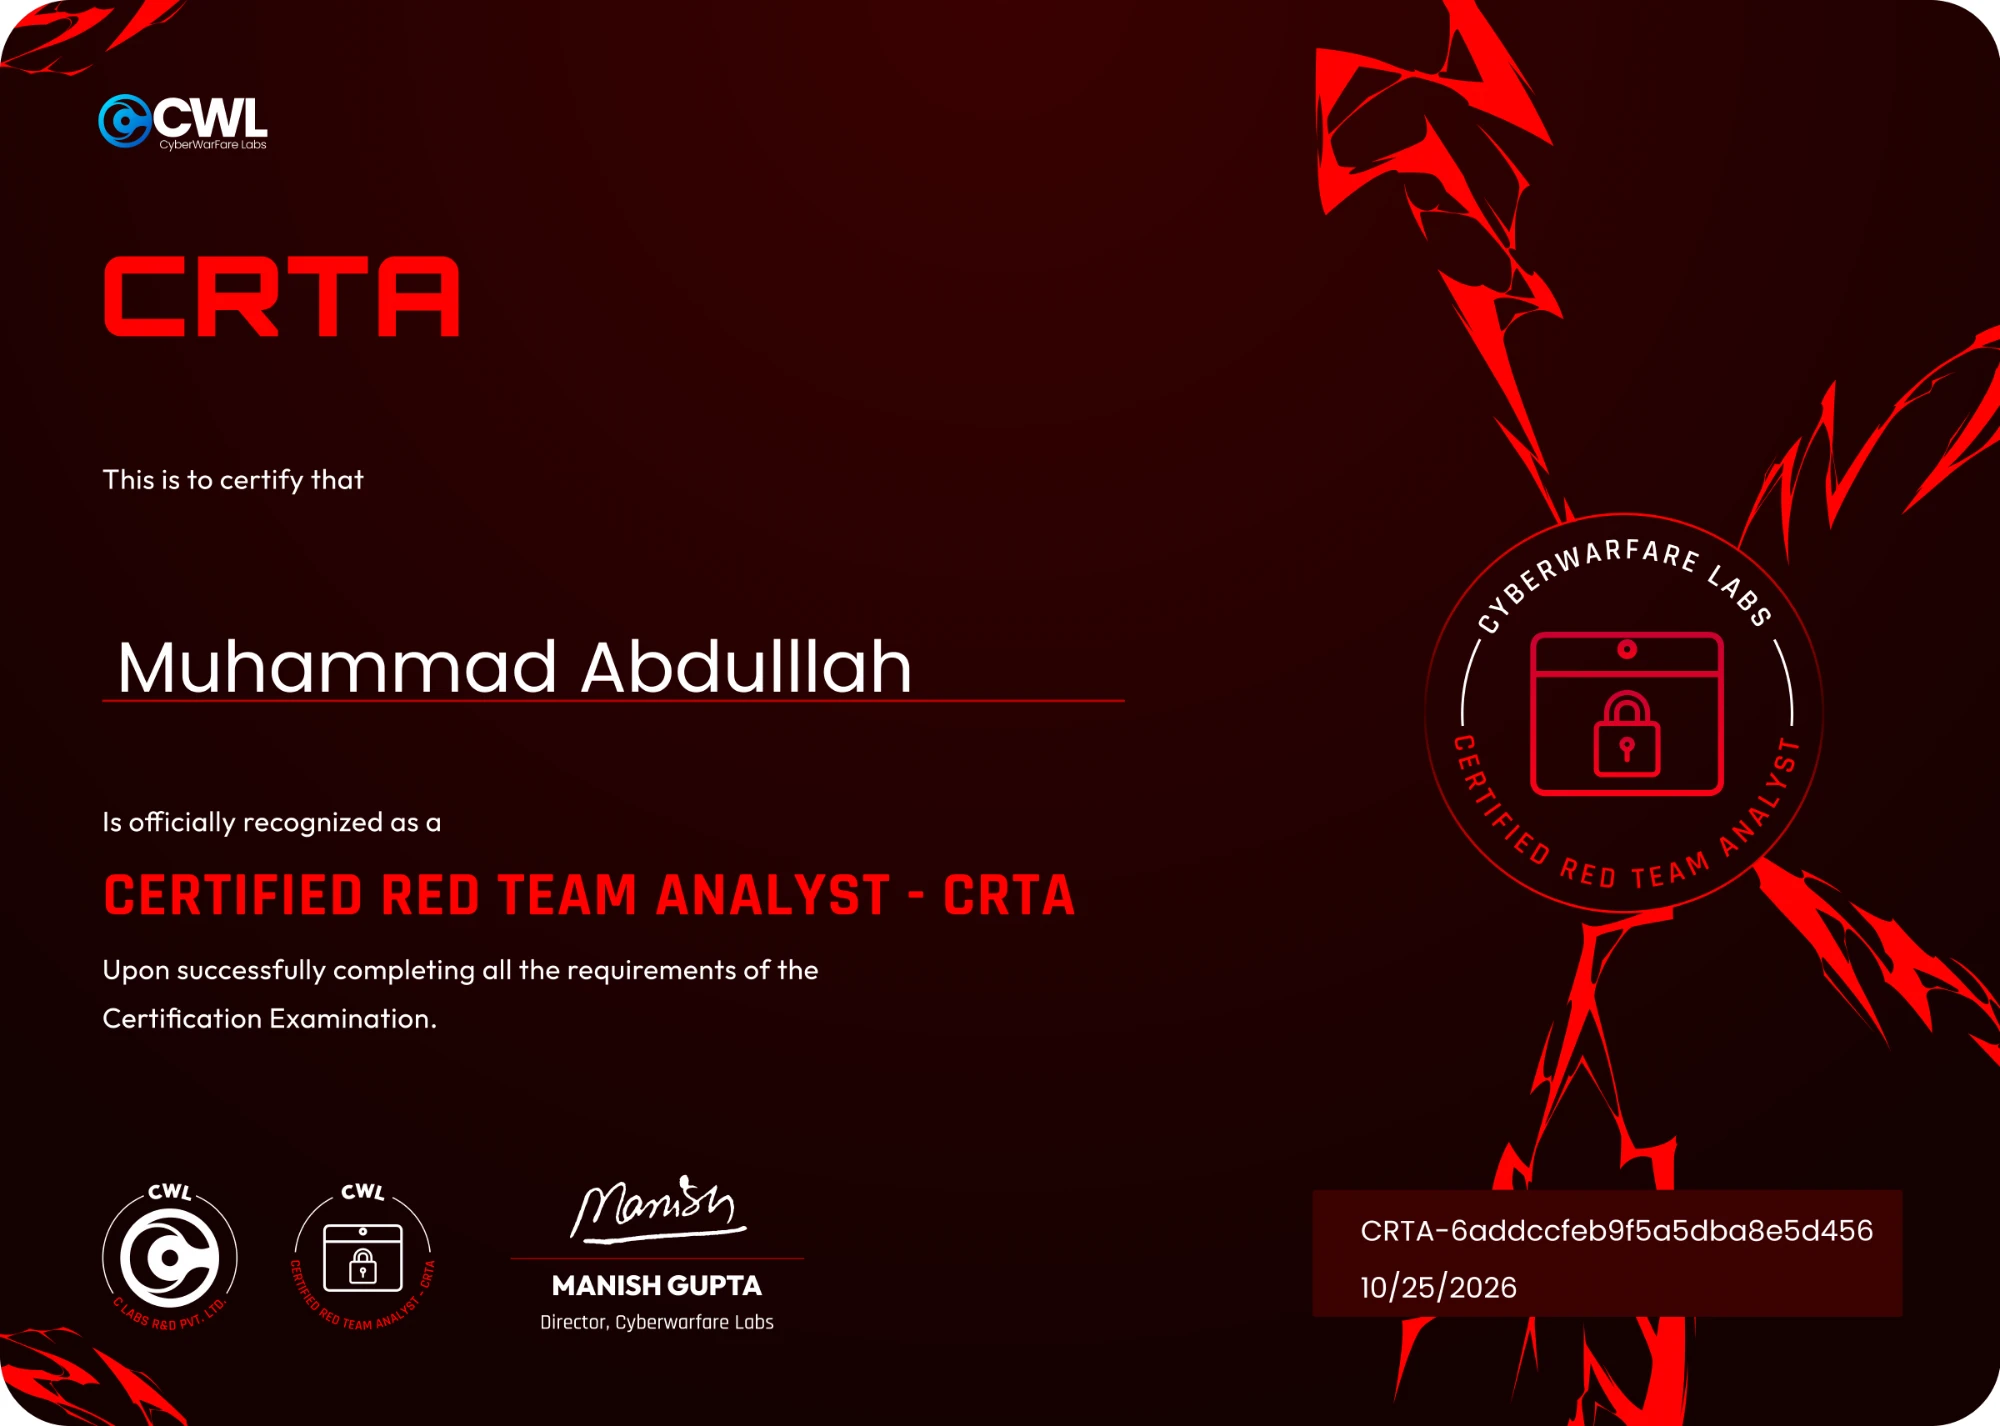
I passed the Certified Red Team Analyst (CRTA) exam by CyberWarFare Labs on October 25, 2026. It cost me $9 with a 90% discount, down from the regular $99.
For about a year before this, I had been practising on TryHackMe and Hack The Box and playing CTFs at local, regional, university, national and international level. I wanted to know where I stand right now, so I used CRTA to find out.
#What helped from my practice
On TryHackMe, I completed Red Teaming, Web Application Red Teaming, Junior Penetration Tester, Web Fundamentals, Cyber Security 101 and AI Security. On Hack The Box, I am around 90% done with the CJCA path.
For this exam, the Red Teaming, Web Application Red Teaming and Junior Penetration Tester paths helped the most, because they cover enumeration, web attacks, Linux, internal networks and Active Directory. Cyber Security 101 and Web Fundamentals gave me the base. AI Security and CJCA were part of my journey, but they did not directly help here.
#How I prepared
The course gives you around 8 hours of video lectures, a 170+ page manual and hands-on labs. I skipped the videos. I skimmed through the manual with Claude to see how CRTA's material matches what I already knew, and that was my final stretch of prep. I only used Claude for this preparation, not during the exam.
#How it felt
It did not feel like an exam to me. It felt like a TryHackMe room at the Red difficulty, the advanced rooms with complex exploit chains and little guidance.
The exam is 6 hours long. If you stay focused, you can finish in 2 to 3 hours. The hard part for me was not stress or getting stuck. It was patience. I did everything by hand in Kali, one command and one tool at a time. Running a tool does not give you something useful straight away. You change the parameters, run it again and look closely at the output before you find something worth following, and only then can you move on.
The one place I slowed down was privilege escalation. I had a foothold on the first Linux machine after a web application weakness let me read local files and find working credentials, and I logged in over SSH. After that I stalled for a bit, until I went back to basic enumeration and checked my sudo rights. That showed me a text editor I could run as root without a password, and escaping to a shell from it gave me root. With root, I looked through the Docker containers and the SSH authentication logs. The logs revealed an internal host that was not in my first scan. That host had an exposed file manager, and a leftover file in it contained Active Directory service account details. Those credentials had replication rights, so I used DCSync to pull the Administrator hash, then passed it over SMB to the Domain Controller and reached the final file. That was the moment everything clicked.
Some people say AI tools can speed this up even more, but I would say do it yourself. It is the only way to find out where your red teaming skills actually stand.
#What you need to know
You need a decent grip on web basics, Linux and privilege escalation, moving through an internal network (pivoting) and Active Directory. You also need to know your basic commands and tools, and be comfortable in the Linux command line.
#What I would change
I would add proper report writing. Right now the exam is flag-based and no report is required, but CPTS and OSCP both ask for one.
Finding vulnerabilities is only half the job. If you cannot explain what you did, that is something to work on. A report would make CRTA feel much more like a real exam, and it could be a very good affordable beginner exam and a stepping stone to CPTS and OSCP. For $9 it was already worth it, but a report would be the cherry on top.
#Takeaways
- Practice first. A year on TryHackMe, Hack The Box and CTFs was my real preparation.
- Skim the course manual to match it to what you already know.
- Do the exam by hand and take your time with each tool's output.
- Learn to explain what you did, even though CRTA does not ask you to.
#What is next
My next targets are CJCA, PNPT, CPTS and CRTO, in that order. After I finish all of them, I will go for OSCP. I will also start job hunting along the way.
If you are preparing for CRTA, feel free to connect or ask me about my experience.