I first checked the provided Python file to see how the flag was encrypted.
cat challenge.py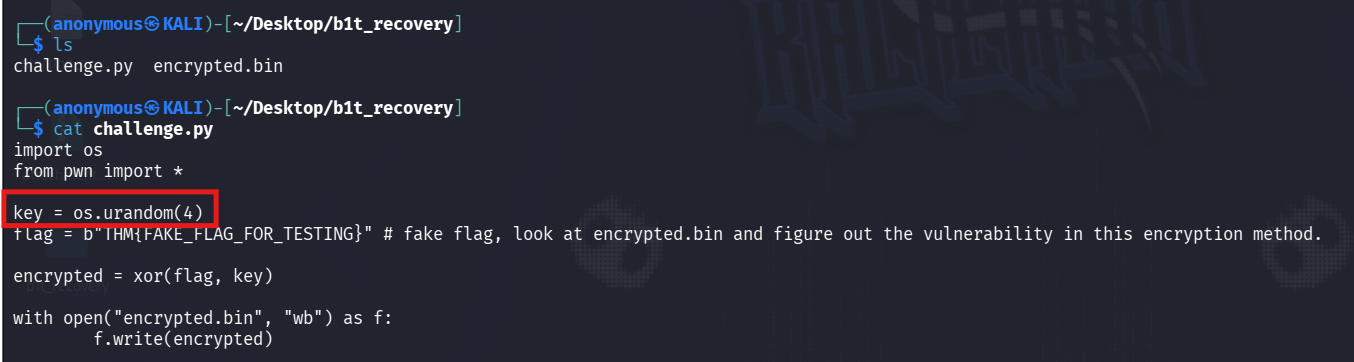
The script uses os.urandom(4), so the XOR key is only 4 bytes long and gets reused across the flag.
Since every TryHackMe flag starts with THM{, I could use those known 4 bytes to recover the full 4-byte key. I wrote a small solve script to XOR the first four ciphertext bytes with THM{, then reuse that key to decrypt the whole file.
from pwn import xor ciphertext = open("encrypted.bin", "rb").read() known = b"THM{"key = xor(ciphertext[:4], known) print("Recovered key:", key.hex()) plaintext = xor(ciphertext, key)print("Plaintext:", plaintext.decode())I ran the script against the encrypted file.
python3 solve.py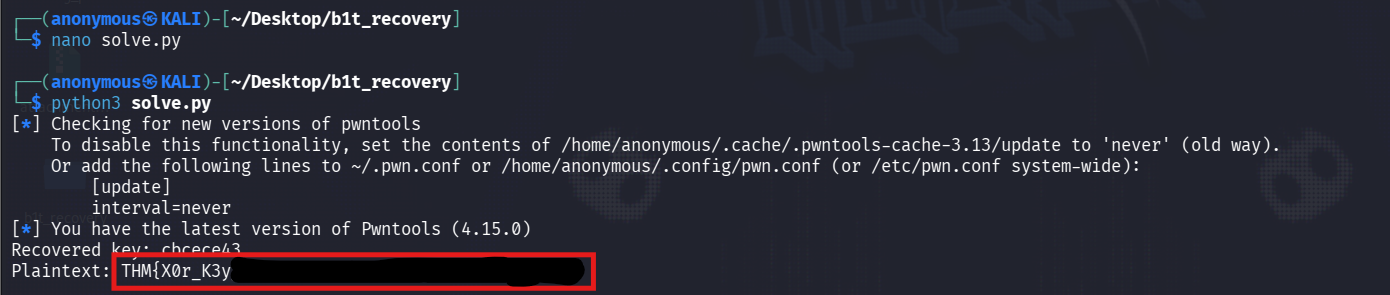
The key was recovered successfully and the plaintext revealed the flag:
THM{X0r_K3y_r3c0verY_***_*****_****_****_****}