Room: Love at First Breach 2026 – Love Letter Locker
An IDOR vulnerability that lets you read other users' private love letters just by changing a number in the URL.
#Recon
Let's do an nmap scan on the target IP:
nmap -sC -sV -p- -T4 10.112.137.43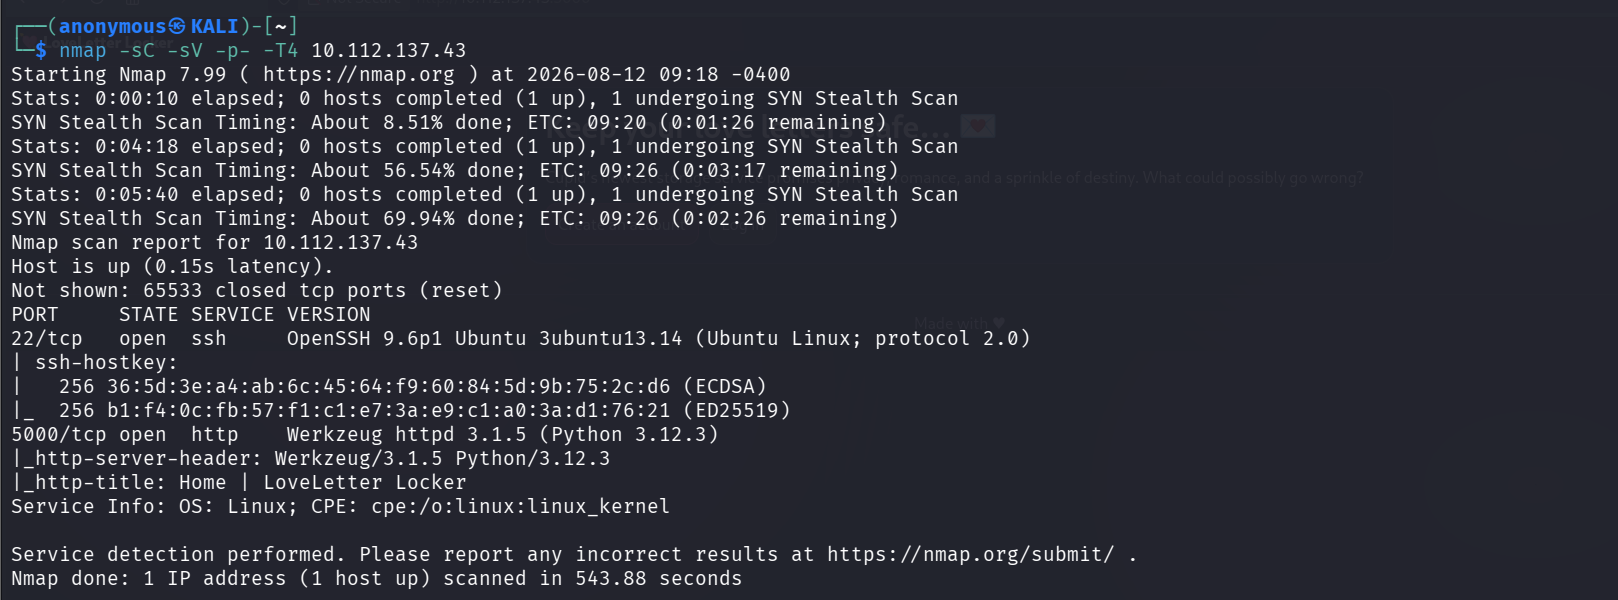
After doing the nmap scan I found 2 open ports which are:
- 22/tcp — SSH
- 5000/tcp — HTTP
#Exploring the Web App
Let's check port 5000 and see what we can do there.
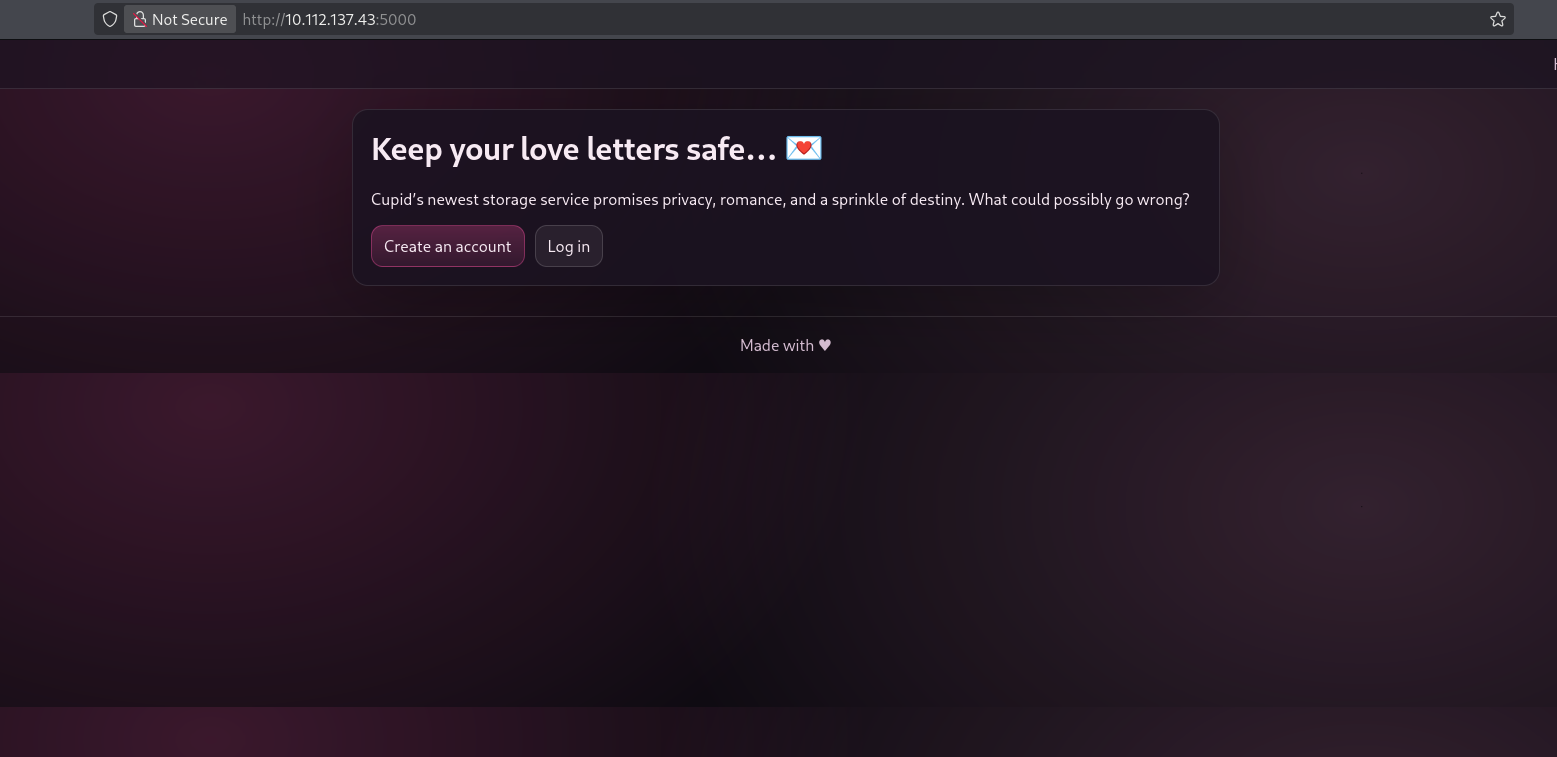
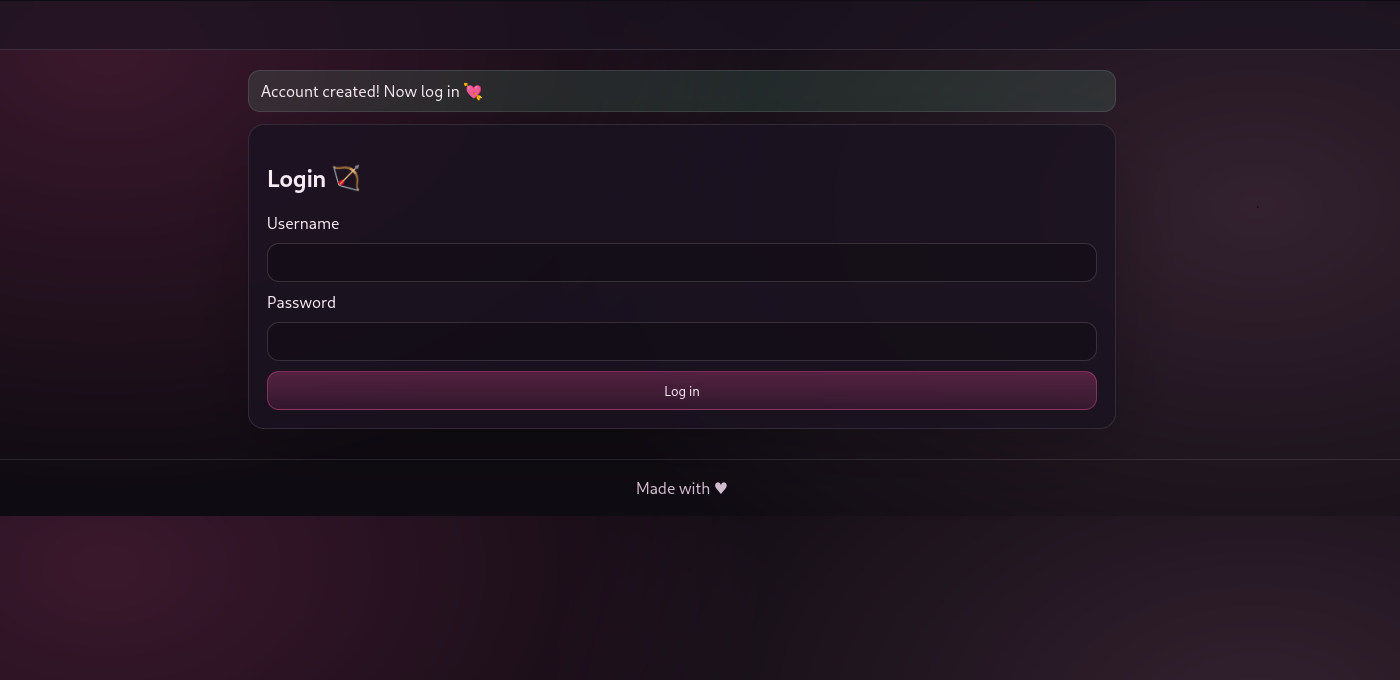
Make an account here and check what we see.
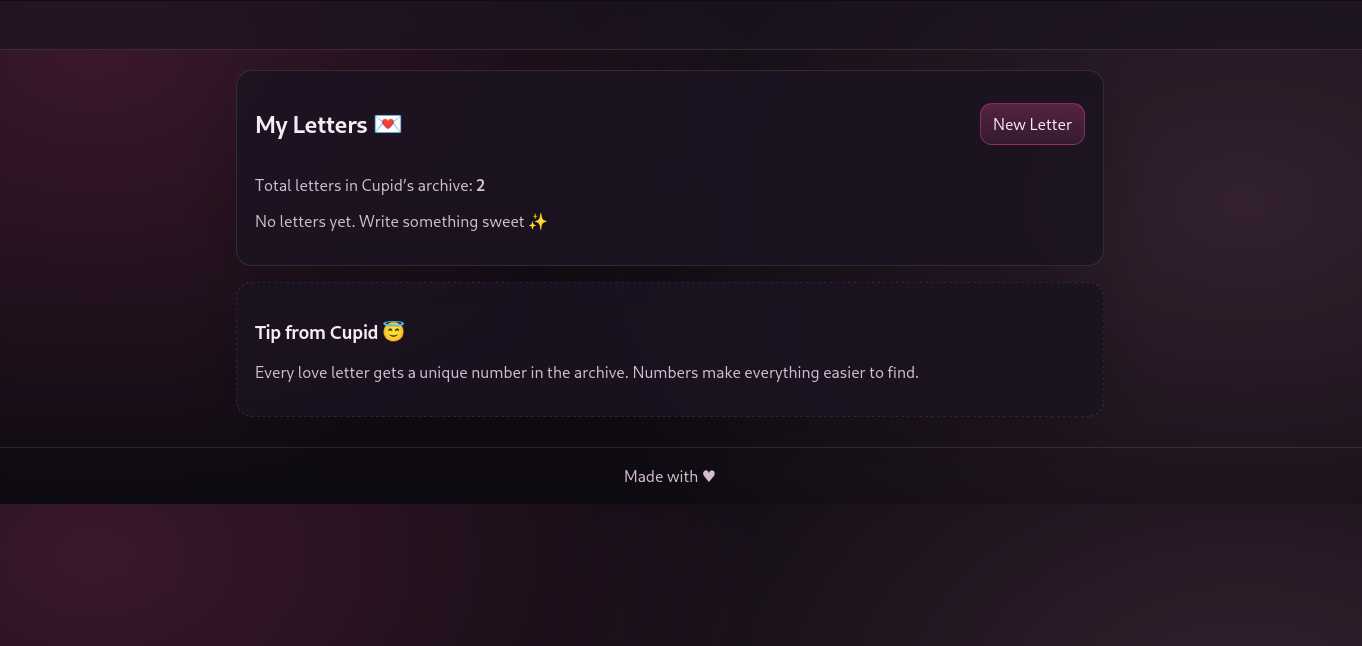
After login we can see that there is a Tip from Cupid that says:
"Every love letter gets a unique number in the archive. Numbers make everything easier to find."
That's a good hint as it tells about the IDOR vulnerability. Let's check where it actually is.
#Finding the IDOR
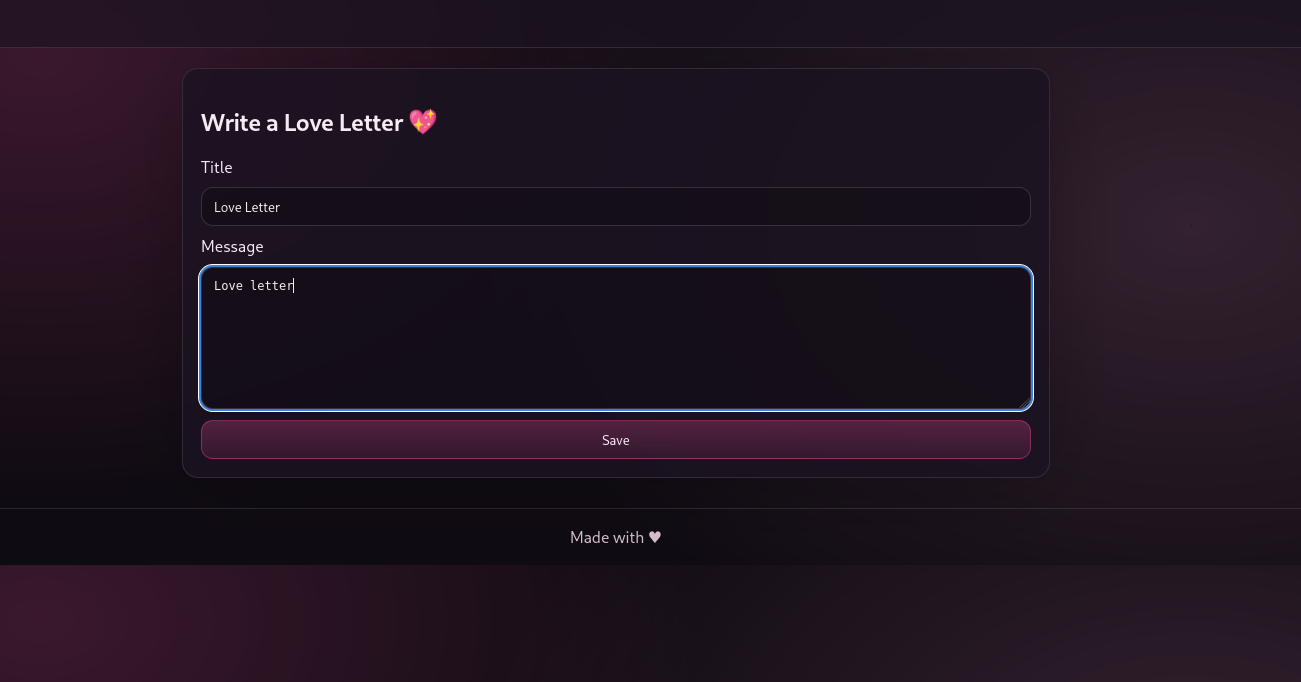
I write a letter just to check what we get from it.
Once the letter is saved, I open it and look at the URL it contains the number 3.
http://10.112.137.43:5000/letter/3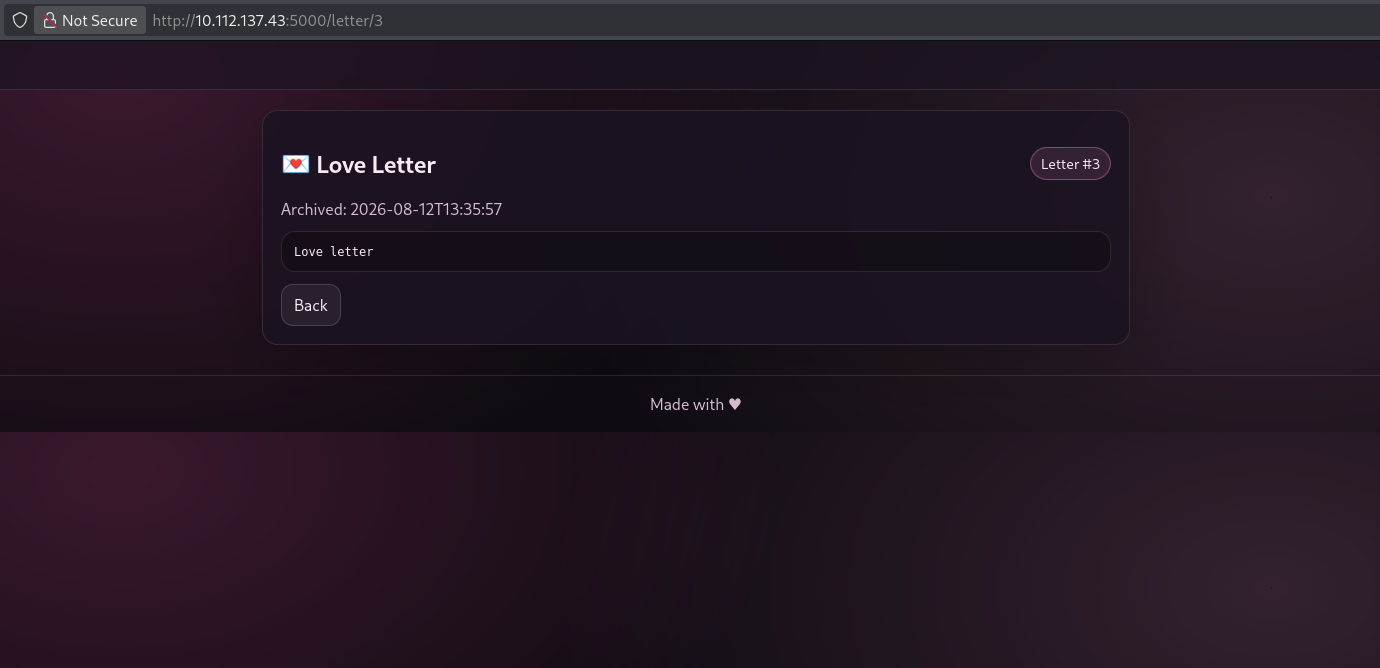
Let's try to change it and check what happens.
When I change the ID to 1, it gives us the flag meaning letter #1 belongs to another user, and there is no access control checking whether the logged-in user actually owns that letter ID.
http://10.112.137.43:5000/letter/1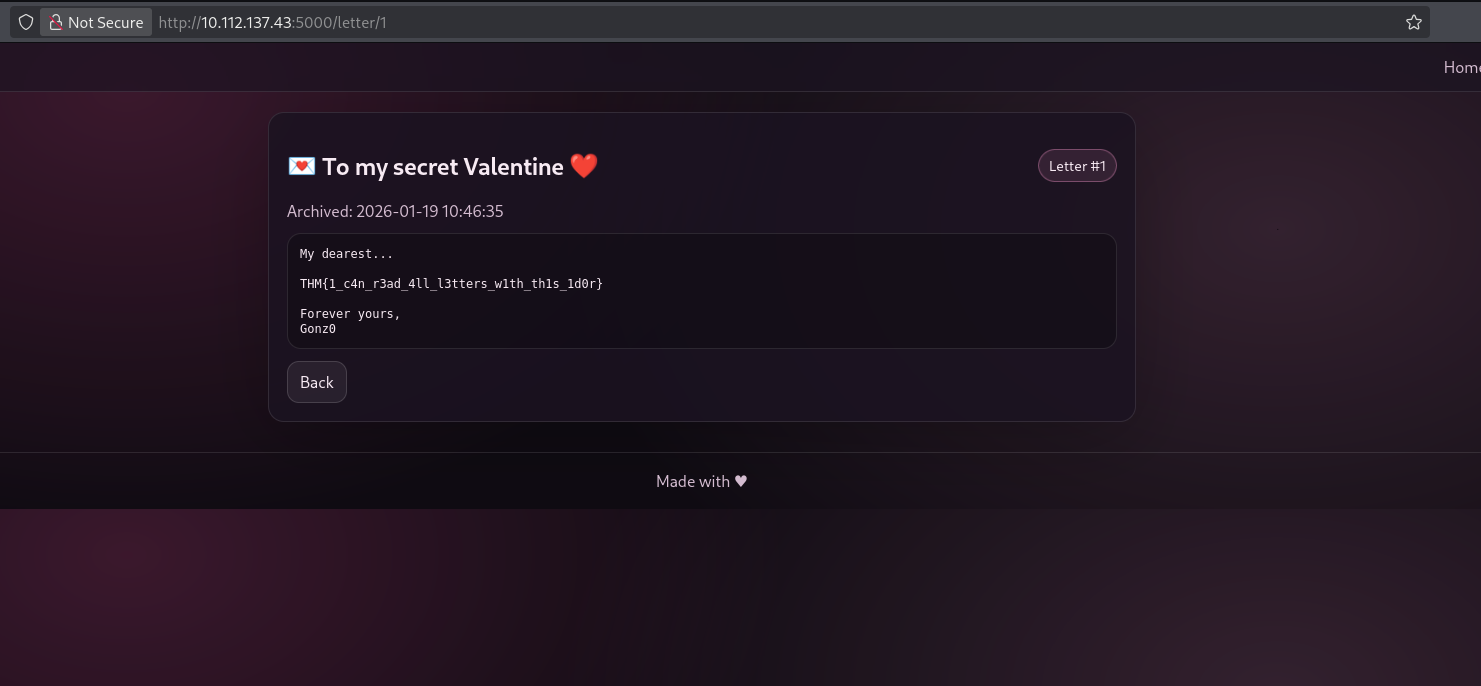
Letter #1 turns out to belong to another user ("Gonz0") titled "To my secret Valentine" and it contains the flag directly in the message body.
#Flag
THM{1_c4n_r3ad_4ll_l3tters_w1th_th1s_1d0r}